Cybersecurity Threats 2026: 7 Proactive Strategies for Protecting Your Digital Assets in the U.S.
The digital realm is an ever-expanding frontier, offering unprecedented opportunities but also presenting an increasingly complex landscape of threats. As we approach 2026, the sophistication and frequency of cyberattacks are escalating, making proactive cybersecurity strategies not just advisable, but absolutely essential for individuals, businesses, and government entities across the United States. The stakes are higher than ever, with data breaches costing millions, reputational damage proving irreversible, and critical infrastructure facing constant assault. This comprehensive guide delves into the evolving threat landscape and outlines seven crucial proactive cybersecurity strategies designed to fortify your digital defenses and protect your invaluable digital assets.
Understanding the contemporary threat environment is the first step toward effective defense. Gone are the days when simple antivirus software and a firewall were sufficient. Today’s adversaries employ advanced persistent threats (APTs), AI-driven malware, sophisticated phishing campaigns, ransomware-as-a-service models, and supply chain attacks that exploit vulnerabilities far beyond an organization’s immediate perimeter. Furthermore, the convergence of IoT devices, cloud computing, and remote work models has broadened the attack surface significantly. In the U.S., regulatory pressures like HIPAA, CCPA, and upcoming federal data privacy laws also necessitate robust security postures, adding another layer of complexity to compliance and protection efforts. Therefore, embracing proactive cybersecurity strategies is paramount for resilience.
This article aims to provide practical, actionable insights into how you can implement these strategies effectively, moving beyond reactive measures to establish a truly resilient and forward-thinking security framework. We will explore each strategy in detail, offering guidance on implementation and highlighting their importance in the context of the 2026 threat landscape.
1. Implement a Zero Trust Architecture (ZTA)
In the traditional perimeter-based security model, everything inside the network was trusted, and everything outside was not. This model is fundamentally flawed in today’s distributed and cloud-centric environments. The ‘Zero Trust’ principle, on the other hand, operates on the assumption that no user, device, or application should be trusted by default, regardless of whether it’s inside or outside the network. Every access attempt, even from within the network, must be authenticated, authorized, and continuously validated. This is one of the most critical proactive cybersecurity strategies for modern enterprises.
Why Zero Trust is Crucial for U.S. Digital Assets
The U.S. government has explicitly mandated a shift to Zero Trust architecture across federal agencies, recognizing its efficacy against sophisticated attacks. For private sector entities, ZTA offers a robust defense against insider threats, lateral movement of attackers, and breaches originating from compromised credentials. By micro-segmenting networks and applying least-privilege access principles, organizations can significantly reduce the impact of a breach, preventing attackers from easily moving from one compromised system to another.
Key Components of ZTA Implementation:
- Identity and Access Management (IAM): Strong authentication mechanisms, including Multi-Factor Authentication (MFA), are foundational. All users and devices must be explicitly verified.
- Micro-segmentation: Dividing networks into small, isolated segments allows for granular control over traffic flow and limits lateral movement.
- Device Posture Validation: Continuously assessing the security posture of devices (e.g., up-to-date patches, antivirus status) before granting access.
- Policy-Based Access: Access decisions are based on dynamic policies that consider context like user identity, device health, location, and the sensitivity of the resource being accessed.
- Continuous Monitoring: Real-time monitoring of all network traffic and user behavior for anomalies that might indicate a threat.
Adopting Zero Trust is a significant undertaking, requiring a cultural shift and a phased approach. However, its benefits in enhancing security posture against evolving threats make it an indispensable element of any comprehensive set of proactive cybersecurity strategies.
2. Enhance Threat Intelligence and Proactive Hunting
Reactive security measures wait for an attack to happen. Proactive threat intelligence and hunting, conversely, involve actively searching for threats within your network before they can cause significant damage. This strategy relies on collecting, analyzing, and acting upon information about current and emerging cyber threats.
The Power of Proactive Threat Hunting
Threat intelligence provides insights into attacker methodologies, indicators of compromise (IOCs), and vulnerabilities being exploited in the wild. By leveraging this intelligence, security teams can proactively search their systems for signs of compromise that automated tools might miss. This includes looking for unusual network traffic, suspicious process executions, or unauthorized access attempts. This is a cornerstone of effective proactive cybersecurity strategies.
Implementing an Effective Threat Intelligence Program:
- Source Diverse Intelligence: Utilize commercial threat intelligence feeds, open-source intelligence (OSINT), industry-specific sharing groups (e.g., ISACs), and internal security telemetry.
- Integrate with SIEM/SOAR: Feed threat intelligence directly into Security Information and Event Management (SIEM) and Security Orchestration, Automation, and Response (SOAR) platforms for automated detection and response.
- Develop Hunting Hypotheses: Based on intelligence, formulate hypotheses about potential attacker techniques and actively search for evidence of these techniques in your environment.
- Dedicated Threat Hunters: Establish a team or allocate resources specifically for threat hunting activities, equipped with advanced tools and analytical skills.
- Regular Reporting and Feedback: Document findings, update security controls, and use insights to refine future hunting efforts.
Proactive threat hunting transforms your security team from defenders into strategists, allowing them to anticipate and neutralize threats before they escalate. This forward-leaning approach is vital for protecting digital assets in 2026.
3. Fortify Supply Chain Security
The SolarWinds attack served as a stark reminder that an organization’s security is only as strong as its weakest link, often found deep within its supply chain. Attackers are increasingly targeting third-party vendors, suppliers, and software components to gain access to larger, more lucrative targets. Strengthening supply chain security is a critical, yet often overlooked, aspect of proactive cybersecurity strategies.
Mitigating Supply Chain Risks
For U.S. entities, the reliance on a global network of suppliers means that vulnerabilities introduced at any point in the supply chain can have cascading effects. This includes everything from hardware components and software libraries to cloud service providers and managed service providers (MSPs). A comprehensive approach is needed to assess and manage these risks.
Key Steps for Supply Chain Security:
- Vendor Risk Assessments: Conduct thorough security assessments of all third-party vendors, focusing on their security controls, incident response capabilities, and compliance adherence.
- Contractual Obligations: Include robust cybersecurity clauses in contracts with vendors, outlining security requirements, audit rights, and breach notification protocols.
- Software Bill of Materials (SBOM): Demand SBOMs from software providers to understand all components (open source and commercial) within the software you use, allowing for better vulnerability management.
- Continuous Monitoring: Implement solutions to continuously monitor the security posture of critical vendors and their adherence to agreed-upon security standards.
- Secure Development Practices: Ensure that your own software development lifecycle (SDLC) incorporates security by design principles, especially if your software is part of another organization’s supply chain.
By proactively addressing supply chain vulnerabilities, organizations can significantly reduce their exposure to indirect attacks and safeguard their digital assets more effectively.
4. Invest in Advanced Endpoint Detection and Response (EDR)
Endpoints – laptops, desktops, servers, mobile devices – remain primary targets for attackers. Traditional antivirus solutions, while still necessary, are often insufficient against polymorphic malware and fileless attacks. Advanced Endpoint Detection and Response (EDR) solutions provide comprehensive visibility, detection, and response capabilities at the endpoint level, making them an indispensable part of proactive cybersecurity strategies.
Why EDR is Essential for Modern Protection
EDR systems continuously monitor endpoint activity, collect and analyze data, and use behavioral analytics and machine learning to detect suspicious patterns that indicate an attack. Unlike traditional antivirus that relies on known signatures, EDR can identify novel threats and actively respond to them, often in an automated fashion. This is crucial for protecting the distributed workforce common in the U.S. and beyond.
Core Capabilities of EDR:
- Continuous Monitoring and Data Collection: Gathers rich telemetry data from endpoints, including process activity, file changes, network connections, and user actions.
- Threat Detection: Uses AI, machine learning, and behavioral analysis to identify anomalous activities and indicators of attack (IOAs) that traditional security tools might miss.
- Automated Response: Can automatically isolate compromised endpoints, terminate malicious processes, or roll back suspicious changes to prevent further damage.
- Investigation and Forensics: Provides detailed forensic data and tools for security analysts to investigate incidents, understand the attack chain, and remediate effectively.
- Threat Hunting Integration: Enables security teams to proactively search for threats across all endpoints using the collected telemetry data.
Implementing a robust EDR solution provides a critical layer of defense, offering deep visibility and rapid response capabilities that are fundamental to maintaining a strong security posture against advanced threats.
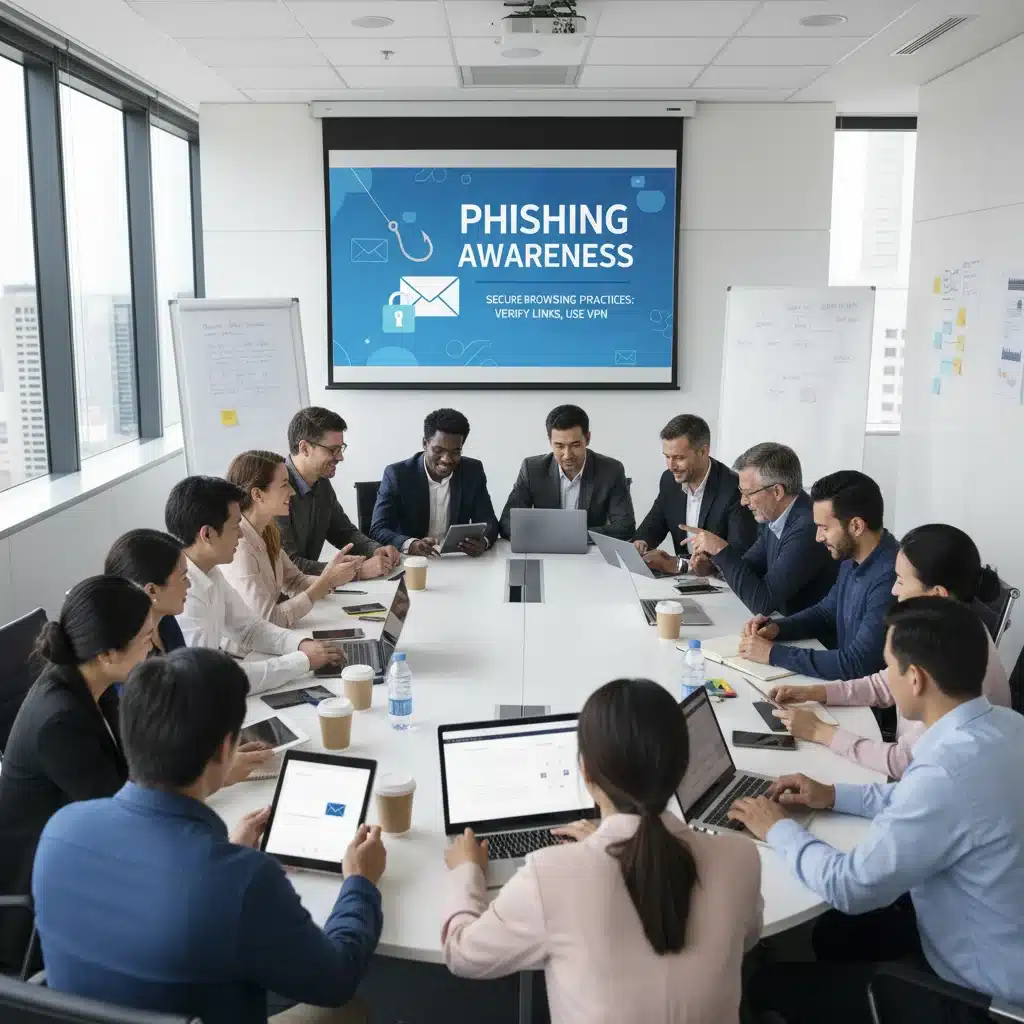
5. Prioritize Security Awareness Training and Culture
Technology alone cannot solve the cybersecurity challenge. Human error remains a leading cause of data breaches. A well-informed and security-conscious workforce is your first and often most effective line of defense. Therefore, investing in comprehensive and continuous security awareness training is one of the most impactful proactive cybersecurity strategies.
Building a Human Firewall
Employees are often the target of social engineering attacks, such as phishing, pretexting, and business email compromise (BEC). Equipping them with the knowledge and skills to identify and report these threats significantly reduces the organization’s risk exposure. A strong security culture fosters a collective responsibility for cybersecurity, where every employee understands their role in protecting digital assets.
Elements of Effective Security Awareness Training:
- Regular and Engaging Training: Move beyond annual, boring presentations. Implement frequent, interactive, and gamified training modules that cover relevant and current threats.
- Phishing Simulations: Conduct regular simulated phishing campaigns to test employee vigilance and provide immediate, targeted feedback.
- Role-Specific Training: Tailor training content to different roles within the organization, addressing specific risks faced by executives, IT staff, or customer service representatives.
- Clear Reporting Mechanisms: Ensure employees know how to report suspicious emails, incidents, or potential vulnerabilities without fear of reprisal.
- Leadership Buy-in: Cybersecurity must be championed by leadership to demonstrate its importance and encourage employee participation.
- Continuous Reinforcement: Use internal communications, posters, and regular reminders to keep security top of mind.
By empowering your employees to be active participants in your security efforts, you create a powerful human firewall that significantly enhances your overall resilience against cyber threats.
6. Implement Robust Data Encryption and Data Loss Prevention (DLP)
Data is the crown jewel of any organization. Protecting it, both in transit and at rest, is paramount. Data encryption and Data Loss Prevention (DLP) technologies are foundational proactive cybersecurity strategies that ensure the confidentiality and integrity of sensitive information, even if other defenses are breached.
Safeguarding Sensitive Information
Encryption renders data unreadable to unauthorized parties, making it useless even if stolen. DLP solutions, on the other hand, monitor, detect, and block sensitive data from leaving the organization’s control, whether intentionally or accidentally. For U.S. businesses handling personally identifiable information (PII), protected health information (PHI), or financial data, these measures are not just good practice but often regulatory requirements.
Key Aspects of Data Protection:
- Comprehensive Encryption Strategy: Encrypt data at rest (e.g., hard drives, databases, cloud storage) and in transit (e.g., using TLS/SSL for network communications).
- Key Management: Implement a robust key management system to securely generate, store, and manage encryption keys.
- DLP Policy Definition: Define clear policies that identify sensitive data types (e.g., credit card numbers, Social Security numbers) and specify how they should be handled.
- DLP Enforcement Points: Deploy DLP solutions across various points: endpoints, network egress points, email gateways, and cloud applications.
- Regular Auditing and Review: Continuously monitor DLP alerts, refine policies, and audit data access to ensure compliance and effectiveness.
- Cloud Data Security: Extend encryption and DLP strategies to cloud environments, leveraging cloud-native security tools and third-party solutions.
By combining strong encryption with intelligent DLP, organizations can create a formidable barrier against data exfiltration and ensure that their most valuable assets remain protected.
7. Develop and Regularly Test an Incident Response Plan (IRP)
No matter how robust your proactive cybersecurity strategies are, a breach is always a possibility. The true measure of an organization’s resilience often lies in its ability to detect, respond to, and recover from an incident quickly and effectively. A well-defined and regularly tested Incident Response Plan (IRP) is therefore not just a reactive measure, but a critical proactive strategy.
The Importance of Preparedness
An IRP outlines the steps an organization will take before, during, and after a cybersecurity incident. It defines roles, responsibilities, communication protocols, technical procedures, and legal considerations. Without a plan, an organization will likely experience chaos, prolonged downtime, increased costs, and greater reputational damage during an attack. For U.S. companies, timely and accurate breach notification is often legally mandated, making a clear IRP indispensable.
Components of an Effective IRP:
- Preparation: Includes establishing an incident response team, defining tools and technologies, creating communication templates, and maintaining up-to-date documentation.
- Identification: Procedures for detecting and confirming security incidents, including monitoring logs, alerts, and user reports.
- Containment: Steps to limit the damage and prevent the spread of an attack, such as isolating compromised systems, disabling accounts, or taking systems offline.
- Eradication: Removing the root cause of the incident, patching vulnerabilities, and cleaning compromised systems.
- Recovery: Restoring affected systems and data from backups, verifying functionality, and returning operations to normal.
- Post-Incident Activity (Lessons Learned): Conducting a thorough review of the incident, identifying areas for improvement, and updating security policies and controls.
- Regular Drills and Exercises: Conduct tabletop exercises and simulated attack scenarios to test the IRP, identify gaps, and train the incident response team.
A well-practiced IRP minimizes the impact of security incidents, reduces recovery time, and demonstrates due diligence to regulators and customers. It transforms potential disaster into a managed event, reinforcing the overall effectiveness of your proactive cybersecurity strategies.
Conclusion: Embracing a Proactive Mindset for 2026 and Beyond
The digital threat landscape in 2026 demands more than just a defensive posture; it requires a proactive, adaptive, and resilient approach to cybersecurity. The seven strategies outlined above – Zero Trust Architecture, enhanced threat intelligence and hunting, fortified supply chain security, advanced EDR, robust security awareness training, comprehensive data encryption and DLP, and a well-tested incident response plan – are not isolated solutions. Instead, they represent interconnected pillars of a holistic security framework.
For individuals and organizations across the U.S., integrating these proactive cybersecurity strategies into their core operations is no longer optional. It is a fundamental requirement for protecting digital assets, maintaining trust, ensuring business continuity, and complying with an increasingly stringent regulatory environment. By investing in these proactive measures today, you are not just reacting to threats; you are building a future-proof defense that can withstand the evolving challenges of the digital age. The time to act is now, to secure your digital future.