Post-Quantum Cryptography: US Organizations’ Urgent 2026 Deadline
The Looming Post-Quantum Cryptography Deadline: What US Organizations Need to Do by 2026 (TIME-SENSITIVE)
The digital landscape is constantly evolving, and with it, the threats to our sensitive data. While today’s encryption methods are robust against conventional computers, a new and formidable adversary is on the horizon: quantum computing. The development of quantum computers capable of breaking current public-key cryptography algorithms is no longer a distant sci-fi fantasy; it’s a rapidly approaching reality. For US organizations, this means a critical, time-sensitive mission: preparing for post-quantum cryptography. The National Institute of Standards and Technology (NIST) has set a de facto deadline of 2026 for the initial transition, making the post-quantum deadline 2026 a pivotal point for cybersecurity strategies across the nation.
This article will delve into the urgency of the post-quantum deadline 2026, explain the quantum threat, outline NIST’s role in standardizing new algorithms, and provide a comprehensive roadmap for US organizations to navigate this complex yet crucial transition. Ignoring this deadline could leave vast amounts of sensitive data vulnerable to future quantum attacks, with potentially catastrophic consequences for national security, economic stability, and individual privacy.
Understanding the Quantum Threat: Why the 2026 Deadline Matters
To grasp the significance of the post-quantum deadline 2026, it’s essential to understand the fundamental shift that quantum computing introduces. Current public-key cryptography, such as RSA and Elliptic Curve Cryptography (ECC), relies on mathematical problems that are computationally infeasible for classical computers to solve within a reasonable timeframe. These problems, like factoring large numbers or solving discrete logarithms, form the bedrock of secure communication, digital signatures, and data encryption globally.
Shor’s Algorithm and Grover’s Algorithm: The Quantum Kryptonite
The game-changer comes in the form of quantum algorithms. Peter Shor’s algorithm, discovered in 1994, demonstrates that a sufficiently powerful quantum computer could efficiently factor large numbers and solve discrete logarithms, effectively rendering RSA and ECC obsolete. This means that any data encrypted today using these algorithms, if intercepted and stored, could be decrypted by a future quantum computer – a concept known as ‘Harvest Now, Decrypt Later’ (HNDL).
While Shor’s algorithm targets asymmetric cryptography, Grover’s algorithm, another quantum breakthrough, can significantly speed up brute-force attacks on symmetric encryption (like AES) and hash functions. While not as devastating as Shor’s algorithm, it still necessitates a review of key lengths and security parameters for symmetric keys.
The ‘Harvest Now, Decrypt Later’ (HNDL) Threat
The HNDL threat is particularly insidious. Malicious actors, including state-sponsored groups, are already collecting vast quantities of encrypted data, anticipating the day quantum computers become powerful enough to decrypt it. This means that even if your data is secure today, it might not be in five or ten years. The post-quantum deadline 2026 isn’t just about protecting future communications; it’s about protecting data that is currently being transmitted and stored.
The Urgency of Quantum Supremacy
While the exact timeline for fault-tolerant quantum computers capable of breaking current encryption remains uncertain, experts generally agree it’s a matter of years, not decades. The rapid advancements in quantum hardware and software development indicate that the threat is moving from theoretical to practical. The post-quantum deadline 2026 reflects NIST’s proactive approach to ensure that organizations have ample time to transition before the threat becomes a reality.
NIST’s Role and the Path to Standardization by 2026
Recognizing the impending quantum threat, NIST launched a multi-year process in 2016 to solicit, evaluate, and standardize quantum-resistant cryptographic algorithms. This initiative is crucial for establishing a new set of cryptographic primitives that can withstand attacks from quantum computers while remaining efficient on classical systems.
The NIST Post-Quantum Cryptography Standardization Process
The NIST process has involved several rounds of rigorous evaluation, with cryptographers worldwide submitting candidate algorithms. These candidates are assessed for their security against quantum and classical attacks, performance, and implementation characteristics. The goal is to select a diverse portfolio of algorithms to address different cryptographic needs (e.g., public-key encryption, digital signatures).
In July 2022, NIST announced the first set of algorithms selected for standardization:
- CRYSTALS-Kyber: For public-key encryption and key-establishment.
- CRYSTALS-Dilithium: For digital signatures.
- Falcon: Another digital signature algorithm.
- SPHINCS+: A stateless hash-based signature scheme, offering a different security trade-off.
NIST continues to evaluate additional candidates for other applications, such as general-purpose encryption and key exchange. The post-quantum deadline 2026 is centered around the expected publication of the final standards for these initial algorithms, which will then trigger widespread adoption.
The 2026 Target: What It Means
The post-quantum deadline 2026 is not a hard regulatory mandate for all organizations, but rather a critical benchmark set by NIST. It signifies the point by which the initial set of quantum-resistant cryptographic standards will be formalized and recommended for implementation. For US federal agencies, compliance will likely become mandatory shortly thereafter, and the private sector will follow suit to maintain interoperability and security best practices. Organizations that handle sensitive data, critical infrastructure, or have long-term security requirements should treat this deadline with utmost seriousness.
A Roadmap for US Organizations: Preparing for the 2026 Deadline
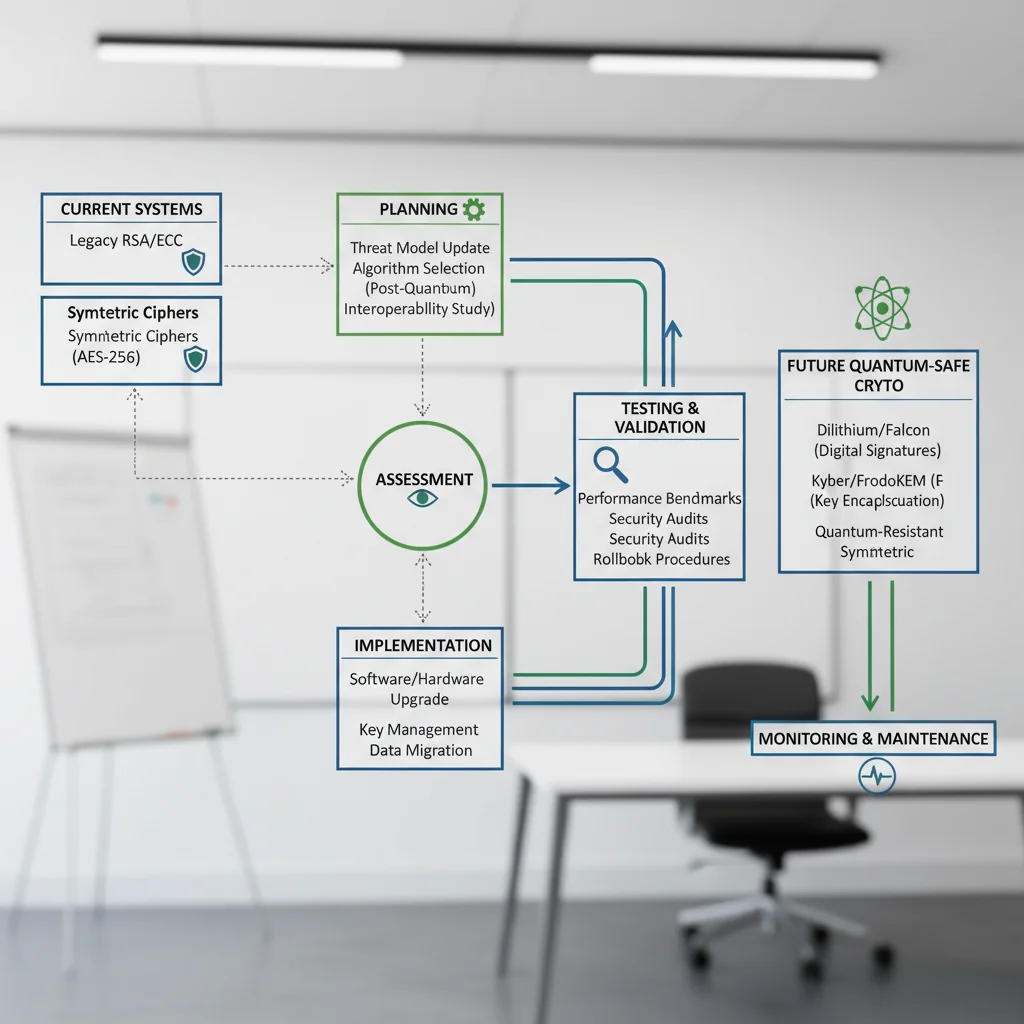
Preparing for post-quantum cryptography is a complex undertaking that requires a strategic, phased approach. It’s not simply a matter of swapping out one algorithm for another; it involves a deep understanding of your cryptographic landscape, extensive planning, and careful execution. Here’s a detailed roadmap for US organizations to meet the post-quantum deadline 2026:
Phase 1: Discovery and Inventory (Immediate Action Required)
The first and most crucial step is to understand your current cryptographic footprint. You can’t protect what you don’t know you have. This phase should begin immediately.
- Identify All Cryptographic Assets: Catalogue every instance where cryptography is used within your organization. This includes hardware, software, applications, protocols, and data stores. Think about:
- SSL/TLS certificates for websites and internal services
- VPNs and secure communication channels
- Digital signatures for documents, code, and transactions
- Encrypted databases and storage systems
- Identity and access management (IAM) systems
- Key management infrastructure (KMI)
- Hardware Security Modules (HSMs)
- Internet of Things (IoT) devices
- Determine Algorithm Usage: For each identified asset, determine which cryptographic algorithms are being used (e.g., RSA, ECC, AES, SHA-256). Pay close attention to public-key algorithms that are most vulnerable to Shor’s algorithm.
- Assess Data Sensitivity and Lifespan: Categorize your data by its sensitivity level and how long it needs to remain confidential. Data with a long confidentiality requirement (e.g., medical records, intellectual property, national security data) is at higher risk from HNDL attacks.
- Map Dependencies: Understand the interdependencies between different systems and applications that rely on cryptographic functions. A change in one area could have ripple effects across your entire infrastructure.
- Identify Third-Party Risks: Extend your inventory to include third-party vendors, partners, and cloud service providers. Their cryptographic practices directly impact your security posture. Inquire about their plans for post-quantum migration.
Phase 2: Risk Assessment and Prioritization (Within 6-12 Months)
Once you have a clear picture of your cryptographic landscape, you can assess the risks and prioritize your migration efforts.
- Quantify Quantum Risk: For each cryptographic asset, evaluate its exposure to quantum attacks based on the algorithms used, data sensitivity, and the potential impact of a compromise.
- Identify ‘Crypto-Agile’ Capabilities: Determine which systems are designed with ‘crypto-agility’ – the ability to easily swap out cryptographic algorithms without major architectural changes. These systems will be easier to migrate.
- Prioritize Migration Efforts: Focus on high-risk, high-impact areas first. This typically includes systems protecting your most sensitive, long-lived data, and critical infrastructure.
- Develop a Phased Migration Strategy: Break down the overall migration into manageable phases. This might involve a ‘hybrid’ approach initially, where both classical and post-quantum algorithms are used concurrently to ensure backward compatibility and test new implementations.
Phase 3: Planning and Design (Within 12-18 Months)
With your inventory and risk assessment complete, it’s time to develop a detailed migration plan.
- Allocate Resources: Secure the necessary budget, personnel, and expertise. This will likely involve a cross-functional team including cybersecurity, IT operations, software development, and legal.
- Engage with Vendors: Contact your software and hardware vendors to understand their post-quantum roadmap. Many will be developing updates and patches to support the new NIST-standardized algorithms.
- Design for Crypto-Agility: If your systems lack crypto-agility, begin planning architectural changes to incorporate it. This will make future cryptographic updates much easier.
- Develop Test Environments: Create sandboxed environments to test new post-quantum algorithms and implementations without impacting production systems.
- Consider Quantum-Resistant Key Exchange: Explore the implementation of quantum-resistant key exchange mechanisms, even for symmetric encryption, to protect against potential future attacks on key agreement.
Phase 4: Implementation and Testing (Leading up to 2026 and Beyond)
This is where the rubber meets the road. Begin implementing and testing the new post-quantum cryptographic algorithms.
- Pilot Programs: Start with small, non-critical pilot programs to gain experience with the new algorithms and identify any unforeseen issues.
- Iterative Deployment: Roll out changes in a phased, iterative manner, closely monitoring performance, compatibility, and security.
- Hybrid Mode Implementation: Many organizations will adopt a hybrid approach initially, running both classical and post-quantum algorithms in parallel. This provides a safety net while new algorithms are rigorously tested in real-world scenarios.
- Performance Benchmarking: Evaluate the performance impact of new algorithms. Post-quantum algorithms can sometimes have larger key sizes or require more computational resources, which might necessitate infrastructure upgrades.
- Security Audits and Penetration Testing: Conduct thorough security audits and penetration tests on your new post-quantum implementations to ensure their robustness.
- Update Policies and Procedures: Revise your security policies, incident response plans, and operational procedures to reflect the adoption of post-quantum cryptography.
Phase 5: Ongoing Monitoring and Adaptation (Post-2026)
The post-quantum deadline 2026 is not an endpoint, but a significant milestone in an ongoing journey. The cryptographic landscape will continue to evolve.
- Continuous Monitoring: Regularly monitor cryptographic usage, algorithm performance, and any new developments in quantum computing or cryptography.
- Stay Informed with NIST: NIST’s post-quantum cryptography project is ongoing. Stay updated on new algorithm selections, recommendations, and any changes in the threat landscape.
- Regular Reviews and Updates: Periodically review your cryptographic strategy and update algorithms as new, more efficient, or more secure options become available.
- Training and Awareness: Ensure your staff are trained on the new cryptographic standards and the importance of post-quantum security.
Challenges and Considerations for US Organizations
While the path to post-quantum cryptography is clear, organizations will face several challenges.
Complexity and Scope
The sheer number of systems and applications that rely on cryptography makes this a monumental undertaking. A comprehensive inventory is often more challenging than anticipated.
Resource Constraints
Many organizations, especially small and medium-sized enterprises (SMEs), may lack the internal expertise, budget, or personnel to effectively manage this transition. Collaboration and leveraging external expertise will be crucial.
Vendor Readiness
The pace of vendor adoption of new NIST standards will vary. Organizations must actively engage with their vendors to ensure their products and services will support post-quantum cryptography in a timely manner. Delays from critical vendors could impact an organization’s ability to meet the post-quantum deadline 2026.
Interoperability
Ensuring seamless interoperability between systems using classical cryptography and those adopting post-quantum algorithms will be a significant challenge, especially during the hybrid transition phase. Standardization and careful implementation are key to avoiding communication breakdowns.
Performance Overhead
Some of the initial post-quantum algorithms may have larger key sizes, signatures, or require more computational resources, potentially impacting performance or increasing bandwidth usage. Organizations will need to assess and mitigate these impacts.
The Role of Government and Industry Collaboration
Meeting the post-quantum deadline 2026 is not solely the responsibility of individual organizations. It requires a concerted effort from government bodies, industry leaders, and academic institutions.
- NIST’s Continued Leadership: NIST’s ongoing work in standardizing algorithms and providing guidance is paramount. Organizations should closely follow their publications and recommendations.
- Government Mandates and Incentives: US federal agencies will likely receive mandates to adopt post-quantum cryptography, which will drive broader market adoption. Incentives for the private sector could also accelerate the transition.
- Industry Working Groups: Collaboration within industry-specific working groups can help share best practices, address common challenges, and develop sector-specific migration strategies.
- Open Source Contributions: The open-source community plays a vital role in developing and testing implementations of new algorithms, making them accessible to a wider audience.
Conclusion: Act Now to Secure the Future Beyond 2026
The post-quantum deadline 2026 is not a date to be ignored. It represents a critical juncture in the evolution of cybersecurity, demanding proactive and strategic action from all US organizations. The threat of quantum computers breaking current encryption is real, and the ‘Harvest Now, Decrypt Later’ scenario means that data being protected today is already at risk from future quantum attacks. The time for deliberation is over; the time for action is now.
By undertaking a thorough inventory, conducting robust risk assessments, developing a phased migration strategy, and actively engaging with vendors and experts, organizations can navigate this transition successfully. The journey to post-quantum cryptography will be challenging, but the cost of inaction – potential data breaches, loss of intellectual property, and erosion of public trust – far outweighs the effort required for preparation. Secure your digital future; begin your post-quantum migration today to be ready for the post-quantum deadline 2026 and beyond.